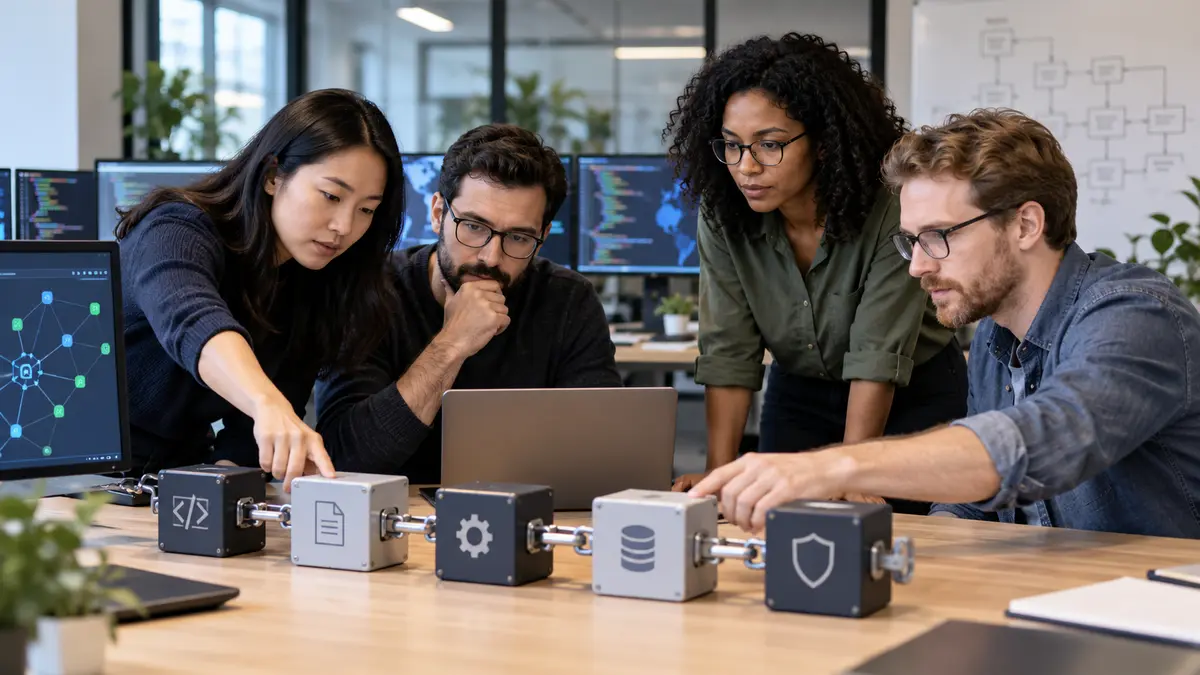
Organizations increasingly depend on libraries, updates and service providers they do not directly control.
Modern software is assembled
Applications incorporate open-source packages, commercial components and automated build systems. A weakness in one dependency can travel into many products.
Visibility is the starting point
Teams need an inventory of important components, update ownership and trusted sources. Unused dependencies should be removed, while critical updates need a tested path to deployment.
Users can ask better questions
Customers cannot audit every line of code, but they can ask vendors about incident response, update policies, vulnerability disclosure and the security of development processes.