A staged approach to identity, devices, access and monitoring without an enterprise-sized security team.
Start with identity and important systems
Require strong multifactor authentication, remove unused accounts and identify the applications holding sensitive information. Smaller organizations gain more from dependable basics than from buying a complex platform without operational capacity.
Reduce standing access
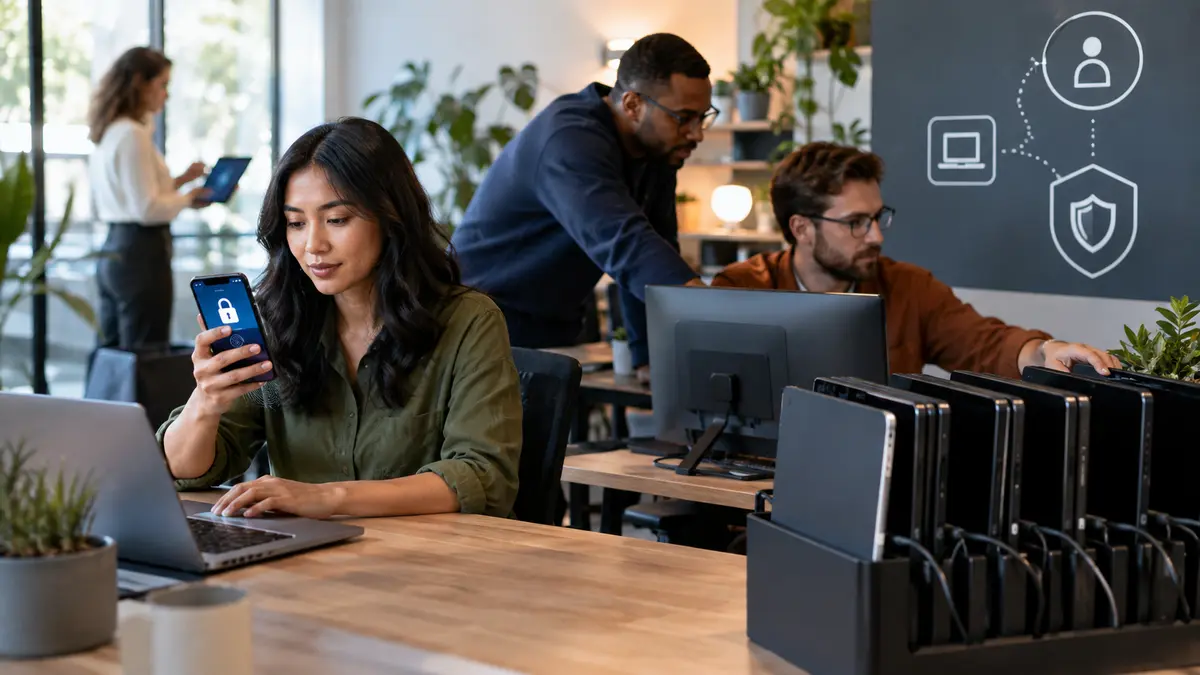
Give people the permissions needed for their role and review privileged accounts separately. Managed devices, passwordless sign-in and conditional access can reduce risk, but rules should include recovery and legitimate travel or remote-work scenarios.
Build visibility and an improvement cycle
Centralize useful sign-in and device alerts, define who responds and practice a small number of likely incidents. Zero trust is not a product or a one-time project. It is a way of making access decisions explicit and continuously reducing unnecessary trust.